Users sign in with their company credentials through AD, Azure AD / Entra ID, Okta or any SAML/OIDC provider.
When the account is disabled in your directory, access to KOŚA is removed automatically and the change is logged.
Get 1 Month Free Trial on DMS & LMS |
One login for your team.
One audit trail for every access.
Connect KOŚA to your Active Directory, LDAP or SSO provider. Manage users and roles centrally, enforce MFA and show inspectors exactly who accessed what — and when.
A live walkthrough built around your process. We reply within one business day.
YOUR USERS. YOUR DIRECTORY.
A tailored walkthrough for your identity and access setup.
30-minute walkthrough · No obligation
Trusted by quality, regulatory & IT teams in pharma, biotech & medical devices
PharmaCorp
BioGenex
MediLabs
CuraVita
NovaPharm
DESIGNED TO SUPPORT
FROM MANUAL ACCOUNTS TO CENTRAL CONTROL
Stop creating and removing accounts by hand in every system. Let your directory drive
who can sign in and what they can do.
Users sign in with their company credentials through AD, Azure AD / Entra ID, Okta or any SAML/OIDC provider.
Directory groups map to KOŚA roles, so permissions follow the person — by site, department or function.
Apply your organisation’s MFA, session and password rules to every GxP module.
Every sign-in, role change and de-provisioning is recorded in a time-stamped audit trail.
of the cost of legacy compliance suites
modules on one validated platform
weeks typical KOŚA implementation
focused walkthrough, no obligation
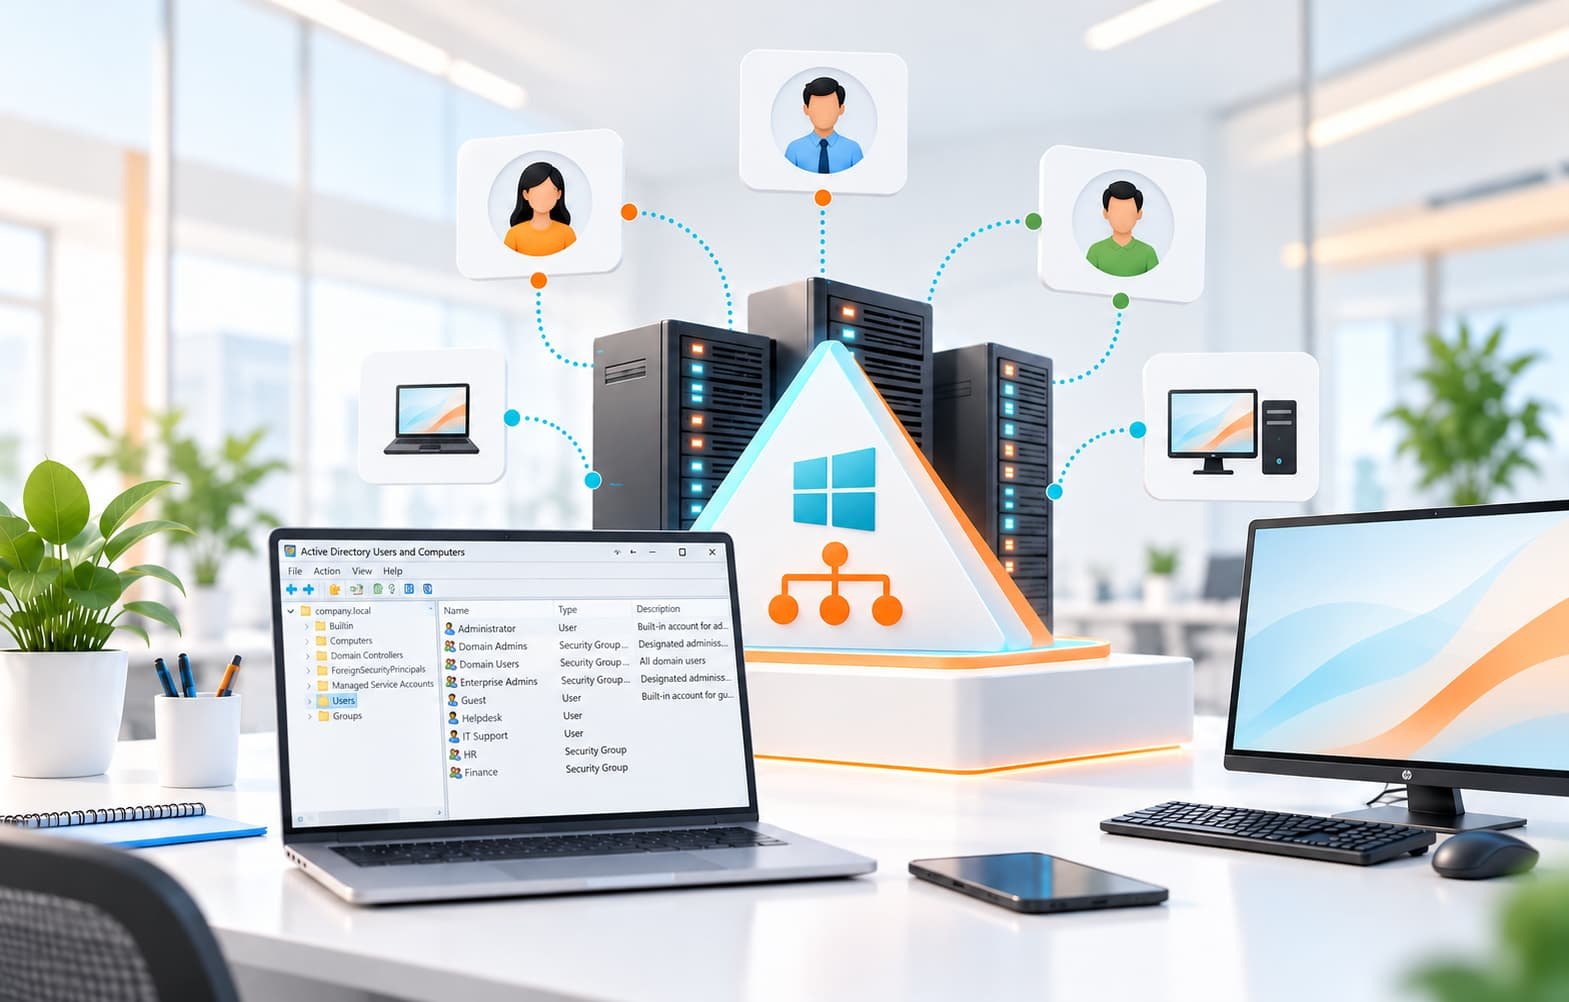
EVERY USER. A CLEAR LIFECYCLE.
Walk through AD/LDAP and SSO setup, group mapping and MFA enforcement.
See how access audit trails and periodic reviews support Part 11 and Annex 11.
Review your identity provider, user volumes, validation and implementation plan.
YOUR DEMO, BUILT AROUND YOUR TEAM
For IT, QA and system owners responsible for access control across GxP systems.
MAKE ACCESS CONTROL YOUR NEXT STEP
One focused walkthrough. Your workflows, systems and compliance priorities.
BEFORE YOU BOOK